






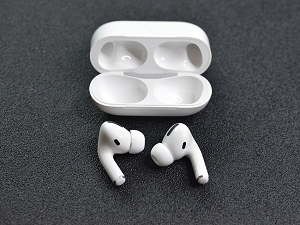
Are you an AirPods Pro owner? Do yours crackle and hiss? If you answered yes to both of those questions be aware that Apple has recently extended the support window for the product. This means that you may be able to get yours replaced for free.
As with most of the products that Apple makes AirPods are cool. They’re also pricey and they’ve had more than their share of development issues.
Given the challenges surrounding the tech Apple announced a service program and pledged to cover any crackling/hissing issues users encountered through October of 2020. In light of the ongoing issues Apple has quietly extended this program for an additional year.
The company did this without any fanfare and no formal announcement. In fact as far as anyone can tell the policy change was first spotted by Reddit users.
If you hear crackling or static sounds on your AirPods, if those sounds increase in loud environments, or if your Active Noise Cancellation feature isn’t working as advertised your gear is probably eligible for replacement.
There are three different avenues you can pursue:
- Contact Apple Support
- Find the Apple Authorized Service Provider closest to you
- Make an appointment with a technician at an Apple Retail Store.
Whatever route you take the technician you ultimately work with will confirm the issue. Assuming you qualify for the program the affected units will be replaced free of charge.
Kudos to Apple for responding quickly to the issues surrounding AirPods Pro and for extending the repair program. We were less impressed with the fact that the program was extended without Apple making a prominent announcement about it.
Here’s hoping that there are no further issues with the AirPod Pro. If it turns out that there are any problems let us hope that Apple will be more vocal about the programs designed to resolve those issues.
Do you use LibreOffice or OpenOffice? If so be aware that security updates have recently been issued due to the recent discovery of a major security flaw. This vulnerability allows an attacker to modify and manipulate documents so that it appears they have been signed by a trusted party.
Although the flaw that makes this possible has only been classified “Moderate” the reality is that the implications could be crippling. Digital signatures are used as a means of verifying that the document in question is from a trusted source. As such the ability to spoof those signatures could easily open the floodgates allowing attackers to do untold harm to any business using either Libre- or OpenOffice.
The OpenOffice flaw is being tracked as CVE-2021-41832 and the LibreOffice flaw is being tracked as CVE-2021-25635. For those who don’t know LibreOffice is a fork of OpenOffice. An offshoot that was created decades ago. That means that this flaw has roots that run deep.
It should be noted that neither of these applications are auto-updating. That means that unless you’re very good about checking for new versions on a regular basis the version you’re currently using is probably out of date. Given the risks that these security flaws represent you should upgrade to the latest version as soon as possible.
If you are unable to upgrade whatever the reason a viable temporary solution would be to disable macros. Also note that if you are running an older version you shouldn’t rely on the “trusted list” functionality. This is because an invalid signature algorithm could still make a laced document appear as it comes from a trusted source.
Kudos to the developers for quickly addressing these security issues. Again if you use either suite be sure you upgrade to the latest version as soon as possible.
Phishing attacks tend to focus on executive level targets. They focus on high ranking targets who have considerable system access.
That appears to be changing. A recent trend tracked by researchers from Avanan has revealed that nearly half of all phishing emails analyzed in recent months were crafted to impersonate non-executives.
Additionally more than three quarters of them (77 percent) targeted employees on the same level.
This is something of a departure and it allows those who orchestrate phishing campaigns to target a significantly larger pool of potential victims. The reason behind the shift in focus is easy enough to understand.
The Avanan researchers summarize it as follows:
“Security admins might be spending a lot of time providing extra attention to the C-Suite and hackers have adjusted. At the same time, non-executives still hold sensitive information and have access to financial data. Hackers realized, there is no need to go all the way up the food chain.”
Increasingly hackers and scammers are coming to rely on spoofed DocuSign emails to gain access.
If you’re unfamiliar with it DocuSign is a legitimate platform used to digitally sign documents. In this case a scammer creates a dummy DocuSign document and emails a request to a low to mid-level employee to update direct deposit information or something similar.
By all outward appearances the DocuSign request looks completely legitimate but there is one important difference. An actual DocuSign email won’t ask the recipient for login credentials. The spoofed ones do. Naturally this is done so that the hackers can harvest those credentials.
Given the crush and volume of daily business emails the difference is easy to overlook which explains why this approach has enjoyed an uncannily high degree of success.
Be sure your employees are aware of this latest threat and stay on their guard against it. One moment of carelessness could wind up being costly indeed.
Do you use Google Chrome on your phone? If so you may have found yourself frustrated more than once by having to tap the “see more results” button because you were unable to find what you were looking for in the first few search results.
If you’ve ever experienced that you will be glad to know that Google is rolling out a change that will do away with the frustrating “see more” button.
Instead you’ll get a continuous scroll feature that will allow you to delve more deeply into the search results until you find exactly what you are looking for. It’s a small change but we regard it as an excellent one.
If you live in the US you may already be seeing the new search behavior. If you don’t see it yet you can expect to see it in the near future whether you’re using an Android or an iOS device. Be aware however that due to the staggered nature of Google’s roll-out the new functionality won’t be available for every search you conduct.
Although this is a relatively small change it’s a very good one that solves one point of frustration a great many users have when surfing the web on their smart devices. It also helps to bring Chrome’s search functionality more in line with modern feed-style apps like TikTok and Instagram.
Google has a long history of going the extra mile when it comes to anything that improves user experience on the web. This is another step in that direction and it follows on the heels of the complete redesign of mobile search Google undertook at the start of 2021.
Kudos to Google for continuing to keep user experience at the forefront of so much of what they do. We think you’ll like the change.
If you use Facebook then you are no doubt aware that recently the company experienced an outage that took the site offline for several hours.
Many people initially assumed that the company had been hacked. However as the outage continued there were none of the telltale signs of an attack. The outage impacted all of Facebook’s tools and not just the site itself which made an attack increasingly unlikely. Even Instagram wasn’t working. Thus the whole of the internet was left guessing.
Facebook engineers of course were busy working behind the scenes tracking the issue down. It has now been corrected. Facebook is up and running again and the company has concluded their investigation into the matter.
Here’s the official word from the company:
“Our engineering teams have learned that configuration changes on the backbone routers that coordinate network traffic between our data centers caused issues that interrupted this communication.
This disruption to network traffic had a cascading effect on the way our data centers communicate, bringing our services to a halt. The underlying cause of this outage also impacted many of the internal tools and systems we use in our day-to-day operations, complicating our attempts to quickly diagnose and resolve the problem.”
The outage couldn’t have come at a worse time. Facebook is under increasing pressure from Congress to increase transparency. Naturally when the outage occurred conspiracy theories were rampant that the company was busily deleting files or otherwise destroying evidence.
Few of these were taken seriously of course but rumors tend to fly when no immediate explanation is forthcoming. This event was no exception.
In any case the issue is now resolved. So if Facebook plays an integral role in the conduct of your business you should be just fine at this point. Kudos to Facebook for the relatively rapid resolution.
Are you a gamer or do you broadcast on Twitch for some other reason?
If so be aware that the platform was recently hacked and the amount of information the attackers made off with is much more substantial than was originally estimated.
Some of the data has now been leaked by an anonymous user on 4Chan.
The share included a torrent link leading back to a data archive that’s a staggering 125GB in size.
Along with the torrent link the anonymous poster left the following message:
“Their community is also a disgusting toxic cesspool, so to foster more disruption and competition in the online video streaming space, we have completely pwned them, and in part one, are releasing the source code from almost 6,000 internal Git repositories.”
Among other things the Twitch data contains:
- Creator payout reports from 2019 to the present day
- SOC Internal Red Teaming Tools
- A Steam competitor from Amazon Game Studios
- A listing of every other property that Twitch owns
- A number of proprietary SDKs and internal AWS services utilized by Twitch
- Twitch clients for desktop, mobile and video game consoles
- Twitch.tv including history dating back to the site’s beginnings
One tidbit culled from the torrent file is the fact that the creators of the hit series “Critical Role” on Twitch was paid more than ten million dollars for their work. That’s a healthy payday for a group of friends playing Dungeons and Dragons together. However unlike some of the other information in the massive archive that’s not damaging.
Out of an abundance of caution Twitch has reset the stream keys for all users. If you stream content of any kind you should have already received an email about it and what steps you need to take next in order to properly secure your account.
Do you have a computer powered by an AMD chipset? Are you excited to upgrade to Windows 11? If you answered yes to both of those questions you should know that at present some AMD processors are struggling to run Windows 11 smoothly.
In fact a few processors have seen performance drops of up to 15 percent which is significant enough to be genuinely annoying.
The good news is that the big brains at Microsoft are aware of the problem and are currently working on a fix.
There are tricky hardware requirements needed to run Windows 11. Microsoft has released an updated version of its “PC Health Check” app which will assist users in determining if or whether their hardware is compatible with the new OS.
Based on statistics collected by Microsoft the roll out of Windows 11 will be substantially slower than the Windows 10 roll out was. That is because at present only about half of registered business workstations are even capable of running the new OS.
It’s also worth mentioning that as things stand now with the new OS machines with more than 8-core processors may experience performance issues. As with the problems with some AMD chips these issues are currently under investigation as well. Before Windows 11 is formally rolled out there’s every reason to believe that those will be resolved.
Windows 10 has been a wildly successful operating system. However just about every longtime Windows user agrees that the menu systems are long overdue for a complete overhaul. That’s one of the many issues that Windows 11 addresses.
Microsoft doesn’t have a good track record when it comes to making truly innovative software. So don’t expect anything groundbreaking from Windows 11. The company will no doubt make a number of excellent incremental improvements and that’s not a bad thing at all.
Google recently announced that they’re planning to auto-enroll some 150 million user accounts into two factor authentication (2FA). The company prefers the term two-step verification (2SV).
The company had this to say about the planned move:
“…because we know the best way to keep our users safe is to turn on our security protections by default, we have started to automatically configure our users’ accounts into a more secure state. By the end of 2021, we plan to auto-enroll an additional 150 million Google users in 2SV and require 2 million YouTube creators to turn it on.”
If you’re not familiar with it, here’s how 2SV works in the Google ecosystem:
You start by logging in with your password. Once the system accepts that you’ll be prompted to confirm your identity via some other means. Here Google has done a great job and offers a number of options including text message to your phone, phone call with a temporary PIN, email with a temporary PIN, or screen tap with an associated smartphone. You can even use an associated iOS device.
This is just the latest move in a long term strategy Google is employing to make the web a safer place to work and play for the company’s legions of users. Although it will surely lead to a bit of grumbling virtually all privacy experts who have weighed in on the matter regard it as a good move and a powerful step in the right direction.
We can reasonably expect Apple, Microsoft, and other major tech companies to adopt similar policies. That means that nearly everyone else will follow suit.
Despite the fact that it’s a minor inconvenience it really is a good move that will make it significantly more difficult to hack into user accounts. It won’t solve the problem but it will put a serious dent in it and that’s a great start.
With the release of Firefox 92 back in September Mozilla made a change that may well doom the browser. If you use Firefox you have probably already noticed it. When you start typing an address you will find sponsored Firefox contextual suggestions in a drop-down list. In simplest terms companies pay a premium to get put on the short list of offered suggestions. This essentially makes the Firefox browser adware.
The company denies this. They claim that they the reason the new feature was added was to help fund the further development and optimization of the browser. Mozilla also stresses that no new data is collected, stored, or shared with the companies on the recommend list or anyone else.
There are a few additional pieces of information to be aware of:
- The company stresses that the only companies on their Firefox’s Suggestions list are carefully vetted by the company.
- Mozilla defines this as a new “discovery feature” designed to enhance the user’s browsing experience
- And that users can opt out by navigating to Settings – Privacy & Security – Address Bar – and Firefox Suggest (then turning the feature off).
It all sounds rather innocuous. At the end of the day Mozilla has decided to display ads. No matter how careful the vetting the list is pay to play. No other major browser on the market today has to resort to such trickery to fund further browser development.
Thus far users have taken a dim view of the addition and it’s hard to see how the company can turn that around. They don’t have an impressive market share as it is and this will certainly drive at least some from the fold. Unless Mozilla has something truly incredible in terms of upcoming features there’s not really any compelling reason to go back to Firefox once you leave.
If you use Firefox and you’re frustrated by the new feature either disable it per the instructions above or give some serious consideration to finding a different browser.
