






The Japanese electronics juggernaut Panasonic is the latest company to fall victim to relentless hackers.
In a recent press release the company indicated their servers had been successfully attacked on November 11th, 2021.
The statement reads in part as follows:
“As the result of an internal investigation, it was determined that some data on a file server had been accessed during the intrusion…
In addition to conducting its own investigation, Panasonic is currently working with a specialist third-party organization to investigate the leak and determine if the breach involved customers’ personal information and/or sensitive information related to social infrastructure.”
The company added that it understands how important their customer data is and they apologized for any inconvenience to their customers.
With the investigation only just getting underway few additional details are available. We don’t yet know exactly how many customers were impacted or what data may have been compromised. We expect that as that information becomes clear the company will be getting in contact with impacted users.
If you are a Panasonic customer and you’ve purchased anything via the company’s website be aware that the hack did occur and that it’s possible some or all of the information in your profile may have been compromised.
At a minimum it would be prudent to change your password right away and monitor whatever debit or credit cards you had saved and associated with that account. That is in case the card details were compromised.
This has been a tough year for Japanese companies which seem to have entered the crosshairs relatively more frequently than companies based in other parts of the world for reasons not yet fully understood. Here’s hoping we get through the rest of 2021 without too many more of these high-profile hacks and that 2022 will be a better year all around.
Have you had your DNA tested by DDC (DNA Diagnostic Center)? If so be advised that the company was recently hacked and that the attackers were able to make off with data impacting 2,102,436 people. According to the company’s disclosure statement the breach occurred between May 24th and July 28th 2021 and the company’s internal investigation into the matter was concluded on October 29th.
The hackers were able to exfiltrate the following data belonging to impacted customers:
- Full Name
- Account Password
- Debit Card Number + CVV number
- Credit Card Number + CVV number
- And Financial Account Number
As bad as that sounds there is still a silver lining. The database that was compromised contained older backups spanning dates from 2004 through 2012 and none of the company’s systems are making active use of that data. So the odds are very good that the account information is out of date.
In all probability the credit and debit card information are out of date too. So to be safe if you have used the service in the past it’s best to review your account and closely monitor whatever credit/debit cards you had attached to your account with the company.
DDC has issued the standard apology to their customers along with a note outlining how much they value the privacy of their customers. That is all well and good. It is small consolation for anyone whose data was compromised and it doesn’t matter whether that data is current or not.
No doubt the company will follow the security recommendations that arise as a consequence of the investigation they’re conducting with a third-party cyber security company. One would hope that at some point we’d start seeing fewer apologies after the fact and better security before. That is especially for a company involved with DNA testing. Here’s hoping.
The UK’s National Cyber Security Centre (NCSC) has identified more than 4,000 different retailers that have been compromised by hackers exploiting known vulnerabilities on checkout pages in order to divert payments and steal payment card details.
The NCSC has been quietly alerting vulnerable retailers over the past 18 months.
Based on the data gathered by the NCSC the majority of impacted retailers were using the e-commerce platform called Magento which is a favored option among small and medium-sized UK retail operations.
Black Friday is the busiest shopping day of the year and it is right around the corner. Therefore the agency wanted to do all that it could to ensure that everyone has a safe and largely uneventful shopping experience with no unpleasant surprises.
In addition to warning UK retailers the NCSC recommends that businesses of all sizes do all they can to secure their sales portals including applying all available security patches in order to minimize risk. That’s good advice no matter where in the world you are and no matter what size your business is.
By now everyone with an online presence is well aware of the fact that web traffic the day after Thanksgiving puts a tremendous strain on the internet. Hackers lurk in almost every corner ready to swoop in and steal what data they can from excited shoppers. Hackers do it hoping people won’t notice the illicit activities they’re doing until it’s far too late to do anything about it.
All too often the assumptions of the hackers prove to be correct. Then unfortunate internet users wind up spending months and hundreds if not thousands of dollars trying to reclaim their identities or pay off debts run up by the hackers themselves.
Don’t let that happen to your customers. If you haven’t already done so conduct a thorough review of your company’s security systems to be sure you’re ready for the holiday rush.
Do you own an iPhone 12 or 13? Have you been dealing with dropped calls? If so then Apple has good news and a fix for that. Simply upgrade to iOS 15.11 and you should be good to go.
15.11 is a minor update that only contains a single entry in the change log. Literally the only thing it does is to improve call performance.
The update isn’t terribly large at just 385MB and even if you haven’t yet experienced any performance or call quality issues it wouldn’t be a bad idea to upgrade in a bid to head them off.
It should also be noted that Apple’s handling of the issue has been absolutely spectacular. Customers complained about an issue and Apple did what Apple usually does. They didn’t spend a lot of time studying the issue. They didn’t complain or make excuses and they simply sprang into action and put people on the task of making it right.
This is the reason Apple customers are so incredibly loyal. In fact it has been said before that Apple doesn’t really have customers they have fans. Die hard absolutely devoted fans. Few other companies in the world can make that claim and everybody wants to replicate the Apple magic.
The good news it that it’s possible. Just be like Apple. Treat your customers like they matter more than anything in the world. Take them and their complaints and suggestions seriously. Go the extra mile and then go a little farther than that when you’re resolving an issue for them.
Apple’s reputation certainly wasn’t built overnight and the company has had their share of missteps but if you’re looking for a company to emulate to strengthen your own you could do a lot worse than Apple. Kudos to the hardworking Apple engineers for knocking another one out of the park.
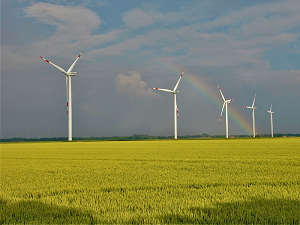
Vestas Wind Systems is one of the leaders in wind turbine manufacturing in North America with 40,000 MW currently installed and another 36,000 MW under service in both the US and Canada.
Recently the company published a breach notification indicating that they had been the subject of a successful cyber attack which occurred on Friday, November 19th.
This forced them to shut down broad swaths of their network infrastructure to keep the attack from spreading. Although Vestas did not specify the exact nature of the attack based on their description it seems likely that the company fell victim to a ransomware attack.
Unfortunately this incident is almost certain to have serious downstream impacts. The company was already struggling with supply chain issues and the shutdown forced them to delay production. That is going to delay the completion of many of the projects Vestas has in the pipeline which will have further impacts as well. Although these are difficult to predict with any accuracy.
According to the latest information provided by the company both the issue itself and the investigation into it are ongoing and the company does not yet have a firm timeline for recovery. Vestas also confirmed that some of the company’s data had been compromised and exfiltrated but did not provide any details as to the specifics of that information.
There have been a number of attacks on critical infrastructure concerns as gangs of cybercriminals seek ever larger payouts. Given that the Vestas attack is very much in line with attacks earlier this year on Colonial Pipeline, Irelands Health Service Executive, and meat processing giant JBS.
If you do business with the company just be aware that their operations have been impacted and that the issue is ongoing so there are almost certain to be delays. Let us hope Vestas is able to resolve the matter quickly.
Are you a GoDaddy customer? Do you maintain a WordPress blog with the company?
If so be advised that the company recently announced a breach of their network. An as yet unidentified third party accessed GoDaddy’s Managed WordPress hosting environment.
Based on the investigation to date the intrusion began on September 6, 2021. While taking advantage of a vulnerability the company was unaware of at the time the unknown attacker was able to gain access to a variety of information.
The information taken includes:
- The email addresses and customer numbers of more than 1 million Managed WordPress customers (both active and inactive)
- The original WordPress Administrative password that was set at the time of provisioning
- For active customers, the SFTP and database usernames and passwords
- And for some customers (exact number unknown at this time), the SSL private key
The company has retained the services of an independent third-party security firm to assist them with their investigation. That investigation is ongoing but the company has already reset the SFTP and database passwords for all impacted users. They are in the process of issuing and installing new certificates for customers who had their SSL private keys exposed.
The company is in the process of contacting all impacted users. If your email address was exposed, you will definitely want to keep a sharp eye out for phishing attacks targeting your email address.
As is the case any time an event like this occurs the company apologized and stressed that they take customer data security very seriously. No additional information is available at this time but bear in mind that the investigation is still ongoing.
It’s unfortunate but not altogether unsurprising. A company as large as GoDaddy with millions of customers is an attractive target for almost any hacker. Stay vigilant out there. This won’t be the last major breach we see this year.
According to a report recently released by Abnormal Security there’s been a huge upsurge of instances of people getting scammed after visiting what they thought were Global Entry, NEXUS, and TSA PreCheck service sites. The issue is that scammers are building very convincing fakes of these types of sites and charging busy travelers $140 for pre-check service. Naturally they are not delivering anything at all after pocketing the money.
The surge in such activity began back in March of this year (2021) but has steadily intensified since then. That’s no great surprise really.
After all with the holiday travel season fast approaching we can conclude that the purpose of the instances earlier in the year were to give the scammers time to refine their approach in advance of the much busier holiday season. They were anticipating a big boost in travel as the pandemic began to recede.
The whole idea behind TSA PreCheck is to streamline the airport screening process and allow travelers to pass through the security checkpoints more quickly once they actually arrive at the airport. Millions of busy travelers have shown a willingness to pay extra for that convenience which is why such sites have increased in popularity since they were first introduced.
You simply enroll in the service, a background check is conducted on you, and you get to travel with minimal hassle from that point forward. Unless you wind up at a fake site set up by the scammers of course.
Then you only think you’re enrolling in the service and the scammers pocket your money and don’t actually do anything. That sets you up for a nasty surprise when you arrive at the airport expecting smooth sailing.
Ahead of the holiday travel seasons scammers are upping their game and sending emails that war of the imminent cancellation of their membership. If they act fast they can “renew” it and have one less thing to worry about when they book their holiday flights.
The key here is to be mindful of the scam and to check the URL of the site you actually wind up at. That’s the giveaway. The scam sites can replicate the overall appearance of TSA PreCheck but they can’t hide the URL.
Sometimes the development process is smooth and sometimes it’s not so smooth. Right now Windows 11’s development is falling into that latter category. Recently Windows Engineers announced a serious issue plaguing the OS.
The culprit was compatibility between the new OS version 21H2 and Intel’s SST (Smart Sound Technology) drivers.
SST is a big deal for Intel. It is an integrated audio Digital Signal Processor (DSP) that was designed to work with the latest Intel Core and Intel Atom processors to handle speech voice and audio interactions.
According to an update on the Windows Health Dashboard:
“The affected driver will be named Intel® Smart Sound Technology (Intel® SST) Audio Controller under System Devices in Device Manager and have the file name IntcAudioBus.sys and a file version of 10.29.0.5152 and earlier or 10.30.0.5152 and earlier.”
The compatible issues are serious enough that they are causing the dreaded BSOD (Blue Screen of Death) errors when they occur. Microsoft has added a compatibility hold to block systems with impacted Intel SST audio drivers from being offered the Windows 11 upgrade (the safeguard ID is 36899911).
The company advises against manually updating Windows 11 but there may be a workaround for some users.
Again per Microsoft:
“To mitigate the safeguard, you will need to check with your device manufacturer (OEM) to see if an updated driver is available and install it. This issue is resolved by updating the Intel® Smart Sound Technology drivers to a version 10.30.00.5714 and later or 10.29.00.5714 and later.
Once you have updated to a compatible version of the Intel® Smart Sound Technology drivers you should be able to upgrade to Windows 11.”
This is par for the course when building new software so events like these should take no one by surprise. Just watch for updates if you’re one of the impacted users. It won’t be long before you’re back to trying out Microsoft’s latest OS offering.
Some months back YouTube announced that it would begin experimenting with the notion of hiding the number of down votes or dislikes that displayed content receives.
At present for most of the content on the platform the number of “thumbs down” votes is displayed alongside the number of “thumbs up” votes that a given video receives.
Having experimented with it for a while now the company has decided to proceed. So you’ll notice a growing percentage of content available that only shows the number of “thumbs up” it gets. Content creators will still be able to see the number of “thumbs down” votes on the back end but those numbers will no longer be available for public consumption.
According to various statements the company has made along the way the goal here is to cut off a potential vector for harassment. Based on the comments found in many videos a significant percentage of users left message saying something to the effect of “I just came here to leave a dislike.”
While there’s merit in the company’s thinking it hides a slightly more selfish purpose as well. In all of YouTube history the single most disliked video is the company’s own “Rewind from 2018” video. In fact that video earned so much negative press that the company has since opted to cancel their Rewind videos altogether.
YouTube is certainly not the first company to make the decision to hide negative rating metrics. Twitter for example allows users to hide the number of likes a tweet gets at the poster’s option.
No matter what your opinion is it is important to stress that as a content creator you’ll still have access to that information. The hope is simply that it won’t be used by viewers to create a negative feedback loop.
