






There was a recently discovered issue with the way the IndexedDB API was implemented in Safari’s WebKit engine.
This is giving IT professionals who work in an environment dominated by Apple products heartburn. The faulty implementation allows or could allow an attacker to intercept leaking browser activity in real time including the user IDs associated with vulnerable machines.
Indexed DB is a commonly used API that has a robust client-side storage system with no capacity limits. Normally it is used for caching web application data so users can view it offline at a later date but of course, it can also be used to store sensitive information.
To prevent data leaks IndexedDB developers followed the “same-origin” policy which controls which resources are allowed to access each piece of data.
Unfortunately, researchers at FingerprintJS discovered that the IndexedDB API doesn’t follow the same-origin policy used by Safari 15 on macOS and the difference in policy could lead to the disclosure of sensitive information.
In order to be impacted by this issue a user has to log onto websites like YouTube and Facebook or visit service portals like Google Keep or Google Calendar. Doing so creates a new IndexedDB database and appends the Google Username.
According to the researchers who first discovered the bug:
“We checked the homepages of Alexa’s Top 1000 most visited websites to understand how many websites use IndexedDB and can be uniquely identified by the databases they interact with.
The results show that more than 30 websites interact with indexed databases directly on their homepage, without any additional user interaction or the need to authenticate. We suspect this number to be significantly higher in real-world scenarios as websites can interact with databases on subpages, after specific user actions, or on authenticated parts of the page.”
Worst of all is there’s no good mitigation strategy here. Disabling all JavaScripts would work but would almost certainly cause other applications to fail that your organization relies on. So we’re waiting on Apple to provide a fix. The good news is that they’ve got a solid reputation for responsiveness so we should not have to wait long.
There’s a new strain of malware called SysJoker to be mindful of. It’s especially dangerous because it can target Windows, Mac or Linux systems. That makes it an equal opportunity strain.
Researchers at Intezer are credited with discovering the malware in the wild in December of 2021 during an investigation of an attack on a Linux server. The group was able to obtain samples of the virus for analysis and have concluded that SysJoker is a nasty piece of work indeed.
Written in C++, the malware strain is cunningly constructed to evade detection on all three Operating Systems. In fact, it’s so good at evading detection that none of the 57 antivirus programs the Intezer researchers tested were able to detect the presence of the malware.
SysJoker is harmless by itself but that is by design. It is a first-stage dropper and its only job is to gain a foothold in a target network.
Once there it will sleep for two minutes before creating a new directory and then copy itself to that directory all while disguised as an Intel Graphics Common User Interface Service (“igfxCUIService.exe”).
According to the Intezer report, this is what happens next:
“…SysJoker will gather information about the machine using Living off the Land (LOtL) commands. SysJoker uses different temporary text files to log the results of the commands,” explains Intezer’s report.
These text files are deleted immediately, stored in a JSON object and then encoded and written to a file named “microsoft_Windows.dll”.”
When that is done, the malware creates persistence by adding a new registry key (HKEY_CURRENT_USERSoftwareMicrosoftWindowsCurrentVersionRun). Random sleep times are interposed between all functions leading to this point.
Finally, it will reach out to the actor-controlled command and control server using a hardcoded Google Drive link. Once that connection has been established, the hackers can install whatever payload they wish onto the infected system.
None of the major AV programs can detect SysJoker at present. Given that it can infect Windows, Mac and Linux systems, this is one to keep a watchful eye out for.
According to the latest Gartner’s statistics, a total of 339.8 million personal computers were shipped in 2021. That was up from 309.1 million in 2020 which amounts to about 10 percent growth in the market.
The company noted that the fourth quarter of 2021 saw a 5 percent drop compared to last year, which may be signaling the end of the pandemic-fueled growth in sales.
Lenovo is the PC maker that has been top of the charts in recent years and they were once again in the top spot accounting for nearly a quarter (24.7 million) of PCs shipped in the year that just ended. HP was not far behind them with a 21.8 percent share, or 74.2 million units shipped. Then we have Dell bringing up the top three scoring 17.6 percent of the market with 59.7 million PCs shipped.
Apple was at the top of the second tier with a 7.6 percent share of the market and shipping 24.3 million units. Acer and Asus rounded out the top six.
The interesting thing about the Gartner analysis is that it stands in stark contrast to rival Canalys’ projection that 2022 will be another year of record PC sales.
As Gartner sees it, the pandemic fueled a one-off, not-to-be-repeated surge in demand and points specifically to the 4th quarter data point as a sign that demand is slowing.
Canalys sees it differently and cites supply chain issues as the main driver behind the 4th quarter slowdown. Canalys insists that demand will remain strong throughout this new year.
Both companies have a very good record when it comes to predicting market moves but only one of them can be right. All we can say is that we currently don’t have enough data to say for sure. Whatever way it shakes out though 2022 is bound to be another interesting year.
Chalk up another first for the hackers. For the first time that we know of, a successful hacking attack caused prisoners in New Mexico to be confined to their cells for a time.
The Metropolitan Detention Center in Bernalillo County, New Mexico went into lockdown on January 5th of this year (2022) when hackers infiltrated the prison system’s network and deployed a malware payload.
For the duration of the system outage the prison cells could not be opened.
While the incident was not reported at the time, details came to light indirectly when the attack and its effects were referenced in court documents. One public defender representing the inmates suggested that their Constitutional rights had been violated due to the incident, which meant that visitations were cancelled.
In addition to the uproar it caused among the prison population, a number of the local government’s databases appear to have been corrupted. Until functionality was restored the employees of the prison could not access camera feeds or access any inmate data.
Of course, the physical keys carried by the guards still worked. However, given the situation, the Warden placed the entire facility on lockdown for the duration of the incident. Full functionality was restored by the afternoon of January 5th.
Few additional details have been revealed about the attack. We don’t even know what sort of malware was deployed. Only that the system is “still being repaired,” according to country officials, and that certain systems are still being impacted.
Unfortunately, the issue has prompted Federal Law Enforcement’s involvement as the prison was already under fire for poor conditions. What happens next is anyone’s guess.
It’s understandable that the county is being somewhat tight-lipped about the incident. That’s especially considering the court case. At least some additional transparency would be appreciated.
For those that aren’t aware, PCI SIG is short for the PCI Special Interests Group.
They have just announced the release of the latest PCI Express (PCIe) specification which is called PCIe 6.0. It has the entire industry abuzz. Standards aren’t usually all that exciting but, in this case, it’s a very big deal.
That’s because it is the specification that matters in terms of connecting your computer’s CPU to graphics cards, SSDs, your Wi-Fi, and the like.
The old 5.0 standard offered transfer rates of up to 64 Giga Transfers per second (64 GT/s). The new standard literally doubles this to a whopping 128 Gigabytes per second in a single direction on 16 lanes (or 8 GB/s per lane). That makes it the largest rate of increase in the entire 19-year history of the standard.
Even better is that the new standard is designed to be backwards compatible so older devices will continue to retain their value.
It’s important to note that as good and exciting as the new standard is, it’s probably too soon to hold off making a strategic purchase to take advantage of it. New products that take advantage of the 6.0 standard won’t hit the market for a few years. So if you need something now, get it. Just know that the day is coming when we’ll all be able to enjoy equipment with significantly improved transfer speeds.
If the past is any guide the first products to be released taking advantage of the new standards were equipment used by server farms and big, industrial concerns. These include research labs that are investing heavily in AI and with consumer products appearing sometime after that.
Even though we won’t be getting any instant gratification from the new standard it’s still fantastic news and points to great things on the horizon.
Google is once again raising the bar where messaging and team meeting software is concerned. The company just rolled out the first phase of its new live translation service for Meet users after months of beta testing the feature.
Naturally this is the first step in a long process, so there are some limitations and caveats to be aware of.
Right now, the translation service only works if you speak English and it can only translate your speech live into four different languages at present. These include French, German, Portuguese and Spanish.
Currently Google and Microsoft are in a bit of a Translation War with Microsoft recently upping their translation game and allowing for real time live captioning of content from English to 27 different languages. The limitation here being that they are not translated from one language to another.
Google may be a bit behind the curve but their goal is to catch up quickly. If history is any guide at all that’s entirely within the realm of possibility. We’ve seen Google move at a blistering pace when the company gets excited about something and they seem determined to catch up with and ultimately surpass Microsoft on the translations front.
All of this is superb news for anyone who has business dealings in various parts of the world where language differences can be a significant barrier to getting anything meaningful done. As Google puts it they see their efforts as equalizing information sharing, learning and collaboration.
It does all those things and more. We are thrilled to see two of the biggest tech firms on the planet pouring so much time and effort into this project. Though world peace is too lofty a goal to consider, if we can at least understand each other, we’ll all be a whole lot better off. Kudos to both Microsoft and Google.
If you have an iPhone by now you’ve almost certainly heard of the security flaw in the HomeKit protocol which allows Apple users to discover and control a wide range of Smart Devices in their home from the HomeKit dashboard. The recently discovered security flaw dubbed “DoorLock” allows an attacker to essentially brick your phone by deploying a maliciously crafted HomeKit accessory name. The issue is being tracked as CVE-2022022588.
Apple has now addressed the issue with the release of iOS 15.2.1 and iPadOS 15.2.1. Both updates improve input validation with the result that the devices are no longer susceptible.
That’s the good news. Trevor Spiniolas is the researcher who first discovered the flaw and he gives us the bad news. The company has known about it since August of 2021, and it has taken months for them to issue a fix for it. During that time Apple said very little about the issue while exposing their user base to unnecessary risk.
Spinolas had this to say about the matter:
“I believe this bug is being handled inappropriately as it poses a serious risk to users and many months have passed without a comprehensive fix. The public should be aware of this vulnerability and how to prevent it from being exploited, rather than being kept in the dark.”
We agree. It does appear that where the DoorLock issue is concerned, Apple dropped the ball. The company is normally much better at handling and responding to issues like these. Here’s hoping they take Spinolas’ criticism in the spirit in which it was intended and strive to do better when the next issue inevitably rears its head.
If you own an Apple device and if you use HomeKit be sure to check your iOS or iPadOS version. If you’re running anything prior to 15.2.1 upgrade right away to mitigate your risk.
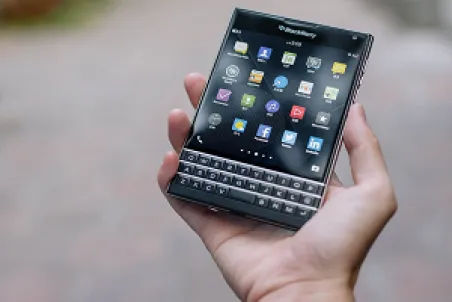
You may find many people who would argue that the iconic Blackberry was ahead of its time. It was in many ways the godfather of the entire smartphone industry. When it was initially released it was an absolute game changer.
Of course, time allowed other companies including tech giants Apple and Google to catch up and ultimately surpass what the Blackberry was capable of. It was clear quite some time ago that the sun had essentially set on the once ubiquitous device.
What you may not have known was that the Blackberry was still supported until very recently. In fact, it wasn’t until September of 2020 that the company announced the formal end of life for the product which was set for January 4 of this year (2022).
That day has now come and gone. At this point the party is officially over for Blackberry. All of its related services including Blackberry Messenger and Blackberry email are now gone.
There’s a short message on the company’s website announcing this fact.
It reads simply:
“As of this date (January 4, 2022), devices running these legacy services and software through either carrier or Wi-Fi connections will no longer reliably function, including for data, phone calls, SMS and 9-1-1 (emergency) functionality.”
It is truly the end of an era and Blackberry was given a Twitter send off as people around the world read the announcement of the final curtain call for the technology. Most of them were speaking in fond and wistful terms about what was a revolutionary piece of technology when it was first introduced.
Farewell Blackberry. You were truly ahead of your time and the digital ecosystem will be a little bit dimmer without you in it. You will be missed.
A research team from Minerva Labs are working in conjunction with the MalwareHunterTeam.
They have recently been tracking a Trojan called Purple Fox and have published a warning about it.
The group behind the Trojan is now distributing their malicious code disguised as a Telegram installation file.
If you’re not familiar with that name Telegram is one of several online messaging apps available on the web. The Trojan has been around since at least 2018 and the hackers who control it have tried a number of different ways to get their malicious code onto unsuspecting desktops.
The use of Telegram as a masking agent is new and the group is also now breaking their malware up into several small files. That makes it less likely to be detected and the researchers have been able to confirm it. They found few AV engines capable of detecting a Purple Fox installation and it is worrisome indeed.
The team behind Purple Fox isn’t resting on their achievements either. They have been steadily adding features and functionality to their code. These new features include a new .net backdoor dubbed “Fox Socket” spotted by Trend Micro in October of last year (2021) and Guardicore Labs discovered a version of the code with wormlike capabilities which allowed the variant to spread with blinding speed.
In addition to that, the malware comes in both 32-bit and 64-bit variants so this one is not to be underestimated. Purple Fox may wind up being one of the biggest threats on the landscape in 2022.
Of course, it’s early days yet and we haven’t seen what other nasty surprises that the hackers of the world have been cooking up over the holiday season, but the bottom line is that Purple Fox is one to watch.
