






Do you own and manage a WordPress site either personally or as part of your business? Do you also use the Tatsu plugin which offers a powerful suite of in-browser editing features and has been installed by more than 100,000 users worldwide?
If so, be aware that there is a serious security flaw in the plugin, and you should update right away to minimize your risk.
The vulnerability in this case is being tracked as CVE-2021-25094 and allows a remote attacker to execute arbitrary code. The developers behind the plugin made a patch available that protects against the exploit, and that patch has been available since April (2022). Shockingly though, only about half of Tatsu’s users have updated their plugin, leaving more than fifty thousand websites around the world still vulnerable.
Finding out if you’re included in that number is easy. Simply check the version of Tatsu you’re running. If you’re running anything from before version 3.3.12, you are at risk and should update as soon as possible.
Independent security researcher Vincent Michel is credited with discovering the flaw, and he made his discovery public on March 28th 2022, releasing proof of concept exploit code along with his disclosure.
The plugin vendor was highly responsive and released a patch less than two weeks later on April 7th 2022. They urged all users to apply the update right away.
Unfortunately, that plea fell on as many deaf ears as responsive ones, which is how we got where we are today.
Wordfence has been tracking the number of times that hackers have made use of this exploit and has observed a large, widespread campaign in progress. The company reports that more than a million attacks have come from just three IP addresses (148.251.183; 254, 176.9.117.218; and 217.160.145.62).
Site administrators are urged to add these IP addresses to their blocklist in addition to updating. It is very good advice.
The Cybersecurity and Infrastructure Security Agency (CISA) has issued an advisory that serves as a stark warning.
If you’re using VMware products that are impacted by recently disclosed critical security flaws, either patch them immediately or remove them from your network.
CISA issued the dire warning because the last time critical security flaws were discovered in VMware products, hackers began exploiting them within 48 hours after they were disclosed.
In this case, the two recently disclosed issues are being tracked as CVE-2022-22972 and CVE-2022-22973, with severity scores of 9.8 and 10, respectively.
The flaws impact the following:
- VMware Workspace ONE Access (Access)
- VMware Identity Manager (vIDM)
- VMware vRealize Automation (vRA)
- VMware Cloud Foundation
- and vRealize Suite Lifecycle Manager
Patches that protect against exploitation of these flaws are already available and VMware is likewise advising customers using the impacted products to apply them as soon as possible, describing the ramifications of delaying as “serious.”
This isn’t the first time VMware’s products have been in the spotlight. Just last month, there were two other flaws (tracked as CVE-2022-22954 and CVE-2022-22960), which impacted the same products.
Although VMware moved quickly in that instance, releasing a patch very quickly, hackers were able to reverse engineer those patches and exploit the flaws anyway.
Worst of all, the security firm Rapid7 has already seen evidence of the exploitation of these flaws in the wild. So every day you don’t patch, you’ve essentially got a target on your back.
CISA has issued the same warning to federal agencies, saying:
“CISA expects threat actors to quickly develop a capability to exploit these newly released vulnerabilities in the same impacted VMware products. Exploiting the above vulnerabilities permits attackers to trigger a server-side template injection that may result in remote code execution (CVE-2022-22954); escalate privileges to ‘root’ (CVE-2022-22960 and CVE-2022-22973); and obtain administrative access without the need to authenticate (CVE-2022-22972).”
Serious issues indeed. Update as soon as possible.
If you’re not familiar with the term, a Zero Day exploit is a security flaw that the software vendor is not aware of and hasn’t yet patched.
In many (but not all) cases, Zero Day Vulnerabilities will also have publicly available proof-of-concept exploits before a patch becomes available. Quite often, these flaws are being actively exploited in the wild.
Apple has recently released a security update to address one of these types of flaws that impact Macs and Apple Watches.
In this case, the flaw in question is tracked as CVE-2022-22675. It is an out-of-bounds write issue that allows apps to execute arbitrary code. That’s bad enough all by itself, but in this case, it allows an attacker to execute that code with kernel level privileges.
The flaw impacts all macOS Big Sur versions before 11.6 and tvOS devices before 15.5.
So far in 2022, Apple has released security patches addressing five different Zero Day exploits.
Here’s a quick summary of those:
- CVE-2022-22587, which allowed attackers to track user IDs and web browsing activity in real time
- CVE-2022-22594, which did the same thing as above
- Then, CVE-2022-22620 was discovered and addressed, which is an exploit used to hack iPads, iPhones, and Macs. This exploit allowed remote code execution and can cause OS crashes
- And in March 2022, two other exploits were addressed. The first, tracked as CVE-2022-22674, is a flaw impacting the Intel Graphics Driver and the second, tracked as CVE-2022-22675, impacted the AppleAVD media decoder.
These five join a long list of Zero-Day exploits the company patched in 2021 that targeted iOS, iPadOS, and macOS devices.
Kudos to the company for their fast action on the Zero-Day front, although the pace of discovery of these types of exploits is distressing to say the least.
In any case, if you own a Mac or an Apple device that uses tvOS, be sure you patch to the latest version right away to minimize your risk.
Phishing campaigns get more effective the more closely they can imitate a trusted source. Recently, security researchers at Fortinet discovered evidence of a phishing campaign that specifically targets Microsoft Windows users and installs three different types of malware on the systems it manages to infect.
Among other things, this campaign gives the hackers behind it the ability to steal usernames, passwords, banking details, and more. That is in addition to leveraging the infected system to secretly mine for cryptocurrency, which finds its way into a wallet controlled by the hackers.
To lure victims into infecting themselves, the Phishing campaign’s contact emails are all designed to appear as a payment report from a legitimate trusted source, which contains an attached Microsoft Excel document. It is conveniently included for the recipient’s review. Naturally, anyone opening the attached document dooms themselves, as it is poisoned and contains scripts designed to install malicious payloads in the background.
Phishing campaigns remain one of the most popular infection methods in the hacking world. They tend to gravitate to those techniques that work and require relatively little in the way of effort.
Phishing fits that bill perfectly. It’s usually a trivial matter to create an email that’s virtually identical to one you might get from a trusted source, and hackers have been poisoning Microsoft Excel files since the earliest days of the internet.
As ever, the best defense against these types of attacks is vigilance and mindfulness. A quick phone call to the trusted source that supposedly sent you the email communication is almost always enough to verify whether it is real. Shockingly, few users take this step.
In a similar vein, clicking on embedded links in an email or downloading files should be done with a healthy dose of caution. That includes another phone call to the trusted source to be sure they did in fact send you something.
Unfortunately, that’s a lot easier to teach than it is to implement, as employees don’t have a good track record with either of those things.
Security researchers employed by Microsoft have recently spotted a variant of the Sysrv botnet. They have dubbed the new variant Sysrv-K.
This new variant works in two ways. First, it exploits a flaw in the Spring Cloud Gateway that allows remote code execution (tracked as CVE-2022-22947). Second, the botnet scans the web for WordPress plugins with older, unpatched vulnerabilities.
Of significance, this variant of the botnet can take control of web servers, which makes it dangerous indeed.
Additionally, Sysrv-K contains new features that the original Sysrv botnet lacked. These include exploits for six different Remote Code Execution vulnerabilities that target the ThinkPHP framework, Drupal CMS, the VMware products XML-RPC, XXL-Job, SaltStack, as well as MongoDB’s Mongo Express admin interface.
Microsoft’s researchers had this to say about their recent discovery:
“A new behavior observed in Sysrv-K is that it scans for WordPress configuration files and their backups to retrieve database credentials, which it uses to gain control of the web server. Sysvr-K has updated communication capabilities, including the ability to use a Telegram bot.
Like older variants, Sysrv-K scans for SSH keys, IP addresses, and host names, and then attempts to connect to other systems in the network via SSH to deploy copies of itself. This could put the rest of the network at risk of becoming part of the Sysrv-K botnet.”
Sysrv-K constitutes a significant threat if you rely on any of the code mentioned above. Be sure your IT Security staff is aware of this new threat so they can prepare for and guard against it.
Sadly, one thing we know for sure about 2022 is that this won’t be the last serious threat we are forced to bring to your attention in a bid to shed light on the latest activities in the hacking world. Stay vigilant out there.
HP recently released a BIOS update to address a pair of high-severity vulnerabilities that affect a wide range of PC and notebook products offered by the company. In both cases, the vulnerabilities would allow an attacker to execute code arbitrarily and with Kernel level privileges.
The two flaws are being tracked as CVE-2021-3808 and CVE-2021-3809 respectively, and both bear a CVSS 3.1 score of 8.8 which makes them both serious issues indeed.
Worse, the two issues impact more than 200 models of HP equipment, including Zbook Studio, ZHAN Pro, EliteBook, ProBook, Elite Dragonfly, business desktop PCs like the EliteDesk and ProDesk, retail PoS computers like the Engage, workstations like the Z1 and Z2, and thin client PCs.
For a comprehensive listing of impacted products, please refer to HP’s security advisory page and scan for the product you own.
Security researcher Nicholas Starke has done a deep dive into both issues.
Starke had this to say about the matter:
“This vulnerability could allow an attacker executing with kernel-level privileges (CPL == 0) to escalate privileges to System Management Mode (SMM). Executing in SMM gives an attacker full privileges over the host to further carry out attacks.”
HP has been having a tough time of things lately. Just two months ago, the company released a BIOS update that addressed sixteen separate flaws. Three months before that, they released a BIOS update that addressed a completely different set of flaws.
Kudos to HP for their time and attention to this matter. However, one has to wonder what has broken down in their core development process that allowed so many serious BIOS flaws to slip through undetected in the first place?
Unfortunately, there’s no word on that but if you haven’t yet applied the latest security update, you’ll definitely want to apply this one as soon as possible.
Do you use a Zyxel firewall? If so, there’s good news. The company has fixed an issue you may not have even been aware that you had.
The company pushed out the fix in a silent update a little over two weeks ago, but when they implemented the push, they didn’t provide many details about it. More of those details are emerging now.
Security researchers at Rapid7 discovered a critical security flaw, now being tracked as CVE-2022030525, which is listed as being a severity 9.8 (critical) issue.
The flaw is described as an unauthenticated remote command injection issue, via the HTTP interface. It impacts all Zyxel firewalls that support Zero Touch Provisioning running firmware versions ZLD5.00 to ZLD5.21 Patch 1.
The following models are specifically impacted:
- USG FLEX 50, 50W, 100W, 200, 500, 700 using firmware 5.21 and below
- USG20-VPN and USG20W-VPN using firmware 5.21 and below
- And ATP 100, 200, 500, 700, 800 using firmware 5.21 and below
According to the company, these products are most commonly found in smaller branch offices and corporate headquarters for SSL inspection, VPN, web filtering, email security, and intrusion protection.
Per the Rapid7 report given to Zyxel on April 13, 2022:
“Commands are executed as the “nobody” user. This vulnerability is exploited through the /ztp/cgi-bin/handler URI and is the result of passing unsanitized attacker input into the os.system method in lib_wan_settings.py.
The vulnerable functionality is invoked in association with the setWanPortSt command. An attacker can inject arbitrary commands into the mtu or the data parameter.”
For their part, Zyxel moved very quickly on the issue. They initially promised to release a fix by June 2022, but quietly pushed out the patch on April 28th, 2022 without supplying a security advisory or other technical details.
We’re not sure why that decision was made, but we’re very pleased to gain access to those details now. Kudos to Zyxel for their rapid response!
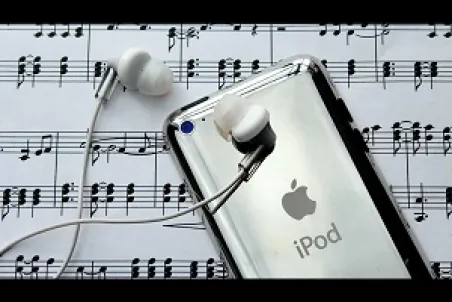
It is the end of an era. Apple recently announced that they were discontinuing the legendary iPod, which is now in its 7th generation of production.
When first released more than fifteen years ago, the iPod was an instant smash hit that almost singlehandedly created the digital music industry, moving it from the shadowy frontier of P2P file sharing services to mainstream respectability.
That’s not bad for a device that costs just under two hundred bucks.
If you don’t yet have an iPod but you feel like you want one, the time to act is now before they’re gone. Although the company has stopped manufacturing new iPods, you can still buy one while supplies last. In case you weren’t aware, the latest version of the iPod is more than just a simple music player – it’s also a surprisingly good digital camera and can even be used as a handheld gaming device.
The 7th generation iPod was released in May of 2019. It sports a fairly powerful A10 Fusion chip paired with a four-inch Retina display and boasts up to 256 GP of storage space.
Apple seldom provides details about why they’ve decided to cancel a given product and they’ve kept with that tradition here, but the reasons are easy enough to guess. Apple was hit particularly hard by the supply chain issues the pandemic caused and given the increase in the capabilities of today’s smartphones, the iPod was increasingly relegated to niche product status.
Even so, it’s a good product and surprisingly versatile. About the only thing you can’t do on it is make phone calls. If that sounds like something you’d be interested in owning, you still have a small window of opportunity to pick one up before they’re gone for good.
Farewell, iPod. You were ahead of your time, and you will be missed.
If you’re a member of the Windows Insiders group, then you are likely already aware of this. If not, here’s something else to look forward to when Windows 11 is formally released. Microsoft has been experimenting with a new “Suggested Actions” feature when you copy data onto your clipboard.
It all begins with Windows 11 build 22621 in the Beta channel and Build 25115 in the Dev channel. There you’ll see the new feature in action any time you copy something to your clipboard. A bar will appear with one or more options, contextualized to the information you just copied.
For example, if you just copied a date in a sentence regarding a conference, you might get a bar that allows you to create an event for that data with a single click. If you copy a phone number, the bar would populate with a button allowing you to place a call to that number with one click or tap and so on.
Currently, the feature is quite limited in its scope, and you only see a “Suggested Action” bar when copying certain types of data. If the feature catches on, it would be easy for Microsoft to expand the idea and potentially to expand it greatly.
At present, Microsoft is actively shopping for feedback about the new feature in the Feedback Hub under Desktop Environment > Suggested action on copy. If enough people respond favorably to the new feature, it’s almost certain that Microsoft will keep it. If enough people write in with suggestions on what other types of data they’d like to see incorporated into the new system, those will most likely be added.
It’s a small thing but this is one way that the user base can help mold the shape and direction of Windows 11 and we’re very pleased to see it. Kudos to Microsoft.
